All WordPress websites Report
Audit
£120
Confirm the PHP version your site actually runs, whether the patch is live, and send a short written report. No changes.
Urgent · PHP2Shell
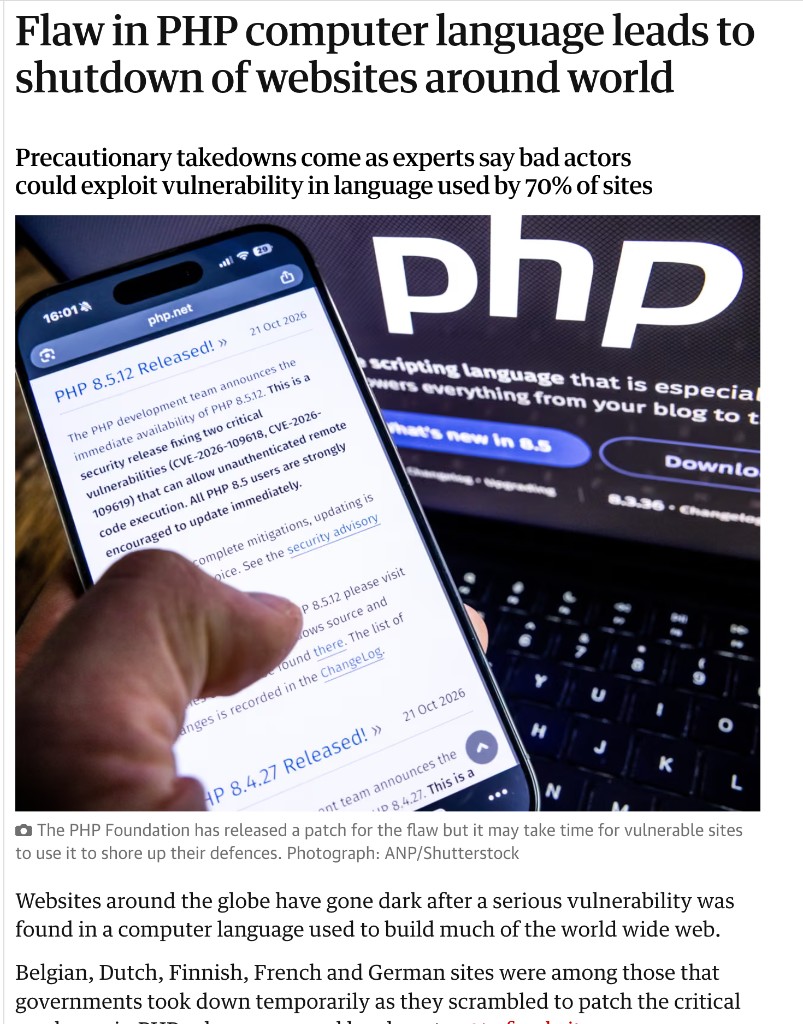
On 21 October 2026 the PHP project released emergency fixes for two critical flaws. They sit in PHP itself — the software that runs WordPress — so updating WordPress will not close them. Unpatched sites can be taken over remotely.
This security breach is affecting all WordPress websites, which run on PHP. PHP helps run around 70% of sites.
This is the PHP incident on BBC News and in The Guardian. Two critical issues in the PHP engine, reported as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), can allow someone on the internet to run code on the server without logging in.
The UK National Cyber Security Centre has called the scale “unprecedented”. The Guardian reports governments took sites offline as a precaution, and that the long tail of websites without ongoing maintenance is what stays exposed. WordPress.org says update PHP immediately. Your host may already be applying the patch. Do not assume they have. Researchers told the BBC that around 90% of at-risk systems worldwide were still unpatched this afternoon.
These flaws sit in PHP itself. An attacker on the internet can run code on the server without logging in. Leaving the site unpatched is not a WordPress delay — it is an open door.
Ask your host, or whoever has panel access, to confirm the full version number. “PHP 8.3” is not enough — it must be one of the builds below.
| PHP branch | Fixed version |
|---|---|
| 8.5 | 8.5.12 |
| 8.4 | 8.4.27 |
| 8.3 | 8.3.36 |
| 8.2 | 8.2.35 |
| 8.1 or older | No official patch. Upgrade to 8.2 or newer. |
In WordPress: Tools → Site Health → Info → Server. Official notice: wordpress.org/news.
Every site is one of three jobs. I confirm which after I look. Each higher price includes the work in the columns to its left. Hack cleanup, if the site is already compromised, is a separate quote.
| What's included | Audit Report £120 | P3 Essential Patch £180 | P2 Upgrade PHP From £450 | P1 Commerce From £650 |
|---|---|---|---|---|
| Written PHP check and report | Included✓ | Included✓ | Included✓ | Included✓ |
| Independent 30-day backup | — | Included✓ | Included✓ | Included✓ |
| Emergency patch | — | Included✓ | Included✓ | Included✓ |
| Version upgrade | — | — | Included✓ | Included✓ |
| Checkout, payments, bookings | — | — | — | Included✓ |
| Who it is for | All WordPress sites | Brochure on 8.2–8.5 | Brochure on 8.1 or older | Payments, shop, or bookings |
All WordPress websites Report
£120
Confirm the PHP version your site actually runs, whether the patch is live, and send a short written report. No changes.
P3 Brochure, already 8.2–8.5
£180
For brochure sites already on a supported PHP branch. Check, independent 30-day backup, apply or confirm the patched build, test, and send evidence of the new version.
P2 Older PHP
From £450
For brochure sites on PHP 8.1 or earlier. Independent 30-day backup, move onto a supported branch, check plugins and custom code, then switch once it is safe.
P1 Payments and data
From £650
For shops, memberships, bookings, or anything holding personal data. Independent 30-day backup, then the patch or upgrade, plus checkout, emails, payment gateways, and booking flows.
The 30-day backup is part of the P1, P2 and P3 work. After that, a monthly care plan from £99 covers ongoing backups, updates, monitoring, and the next emergency without a panic invoice. Tick the form if you want that quoted.
I reply within one working day with the agreed package and how to share access.
You share hosting and WordPress access (password manager, temp admin, or hosting invite). I take a complete files-and-database backup, store it away from the live host for 30 days, and check it can be restored.
PHP is patched or verified. You test the live site. I send a one-page report: old version, new version, and where the independent backup is held.
Five short steps. Do not enter passwords. If you cannot finish it now, email josh@outpost.studio.
I have your authorisation and will reply within one working day.
While you wait: do not email passwords. If you use a password manager, keep it ready. If you would rather brief your host yourself, ask them to confirm the full PHP version in writing (for example 8.3.36, not “8.3”).